


EU CRA Readiness for Smart Kitchen Appliance Importers
A connected air fryer can pass electrical safety and EMC testing yet still be unprepared for the EU Cyber Resilience Act. The gap often appears outside the physical appliance: no clear owner for the app, no controlled firmware record, no vulnerability intake process, and no agreed security-support period.
This matters now. On July 27, 2026, the European Commission published new non-binding guidance explaining CRA scope, substantial modification, support periods, risk assessment and reporting. For kitchen appliance buyers, the immediate task is not to become cybersecurity engineers. It is to decide who carries the legal role, which connected functions are in scope, and what evidence must exist before a supplier or SKU is approved.
The central sourcing decision is this: do not release a connected private-label appliance for mass production until the product owner, software owner, reporting contact and support obligations are documented across the complete supply chain.
Key Takeaways
- An EU private-label business selling a connected appliance under its own name or trademark may be the CRA manufacturer, even when a non-EU factory builds the product.
- CRA reporting obligations apply from September 11, 2026; the main product requirements apply from December 11, 2027.
- Reporting duties can affect connected products already available in the EU before full application in 2027.
- Supplier approval should cover software ownership, risk assessment, vulnerability handling, support period, update control and technical documentation.
- CE files for electrical safety, EMC or radio compliance do not by themselves demonstrate CRA readiness.
What Changed on July 27, 2026?
The Commission's new guidance does not replace Regulation (EU) 2024/2847 and is not legally binding. Its value is practical: it addresses questions businesses have been asking about which products fall within scope, when a change becomes a substantial modification, how support periods should be determined, and how manufacturers should approach reporting and cybersecurity risk assessment.
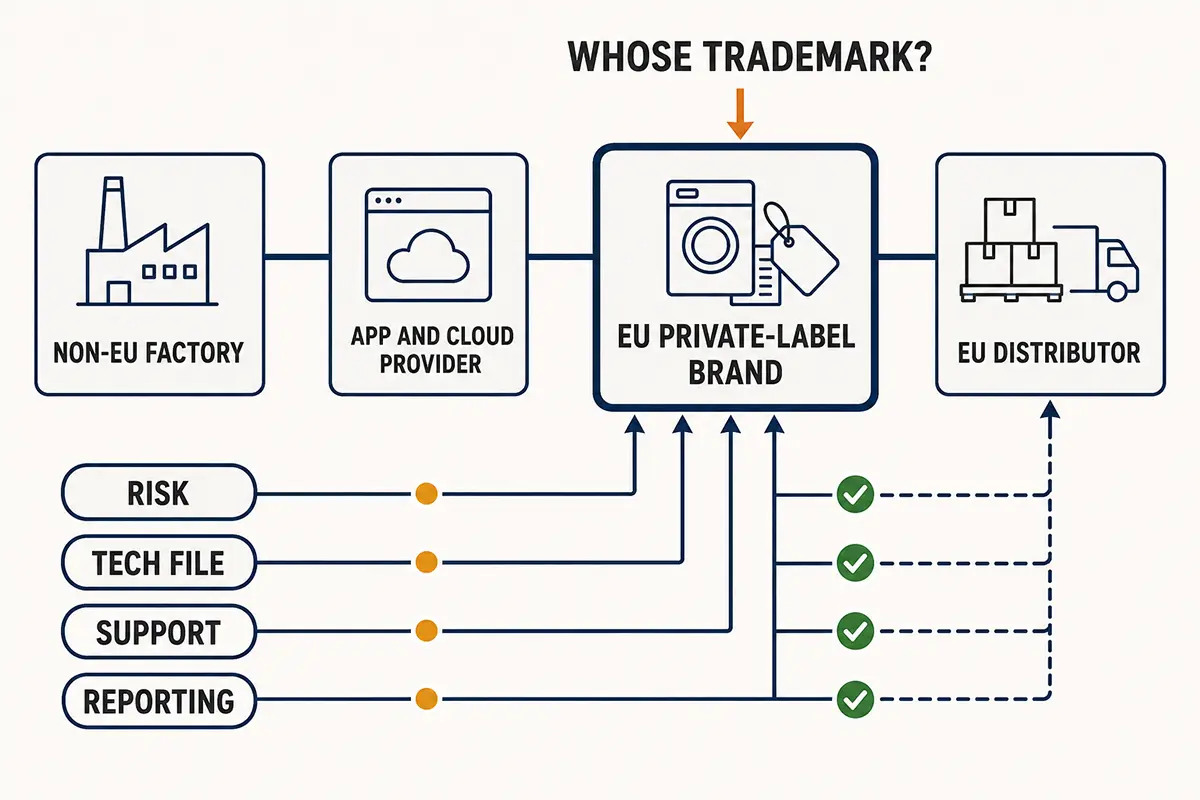
That clarification is especially relevant to OEM and ODM kitchen appliance projects. A typical connected product may involve an appliance factory, controller-board supplier, firmware developer, mobile-app provider, cloud platform and European brand owner. CRA responsibilities cannot be managed if each party assumes another supplier owns the software evidence.
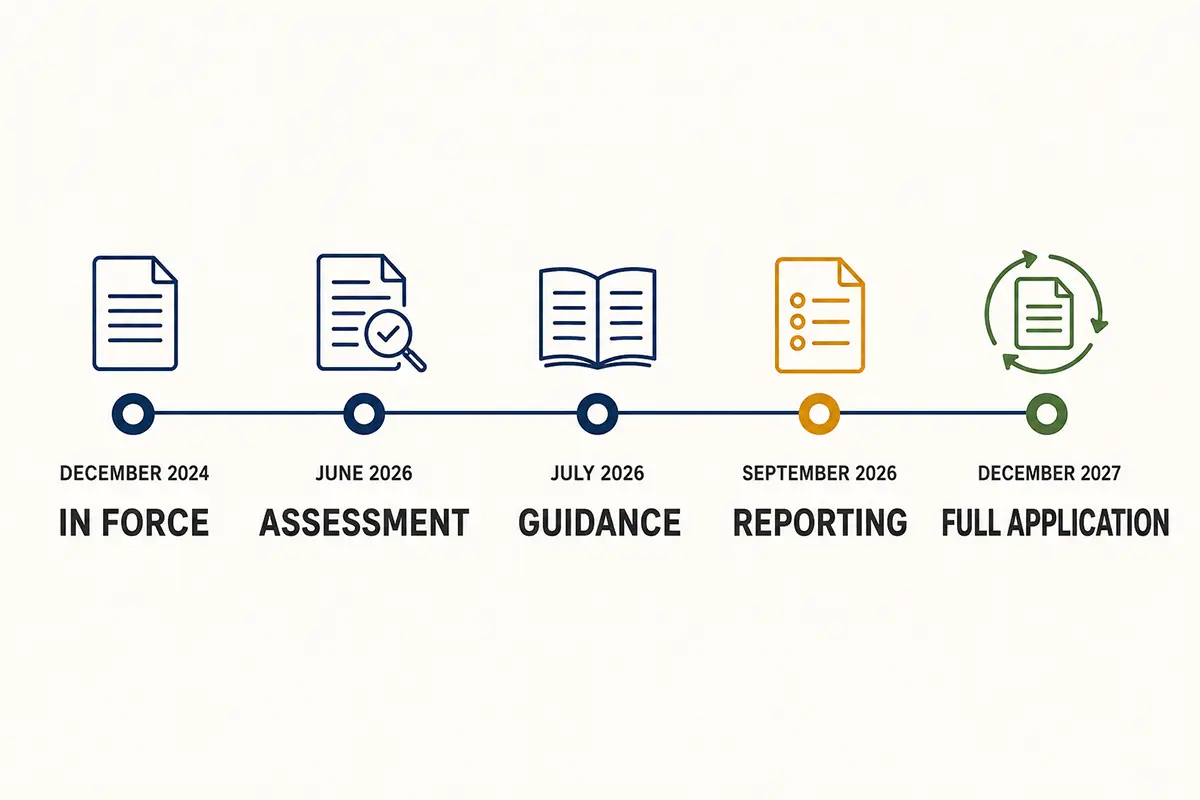
The Commission also confirms a transition that buyers should treat as two separate gates:
| Date | CRA Milestone | Practical Buyer Action |
|---|---|---|
| December 10, 2024 | CRA entered into force. | Add CRA ownership to connected-product planning rather than treating it as a future lab task. |
| June 11, 2026 | Rules on notification of conformity assessment bodies began to apply. | Confirm the assessment route for the specific product category instead of assuming every product follows the same route. |
| July 27, 2026 | Commission issued its first implementation guidance. | Review scope, support-period and substantial-modification assumptions against the new guidance. |
| September 11, 2026 | Article 14 reporting obligations begin. | Ensure the legal manufacturer has a reporting owner, escalation path and access to technical facts. |
| December 11, 2027 | Main CRA obligations apply. | Place only compliant in-scope products on the EU market and maintain lifecycle vulnerability handling. |
First Decide Your Legal Role
The words used in a commercial contract do not automatically determine the CRA role. Under the Regulation, a manufacturer includes a business that has a product with digital elements designed or manufactured and markets it under its own name or trademark. An importer is an EU-established business that places on the market a connected product bearing the name or trademark of a business established outside the EU.
This distinction is critical in private-label sourcing. A European retailer that asks an overseas factory to manufacture a Wi-Fi air fryer under the retailer's own brand may fall within the manufacturer definition. Calling the retailer an "importer" in the purchase order does not remove manufacturer obligations.
| Commercial Situation | Likely CRA Role to Review | What the Buyer Must Clarify |
|---|---|---|
| EU brand sells a connected appliance under its own trademark. | Manufacturer role may apply. | Who owns risk assessment, conformity assessment, technical documentation, support and reporting? |
| EU company imports a connected appliance bearing a non-EU manufacturer's brand. | Importer role may apply. | Has the manufacturer completed the required assessment, documentation, marking and vulnerability processes? |
| EU wholesaler resells an unchanged connected appliance already placed on the EU market. | Distributor role may apply. | Are marking, contact details, instructions and support-period information present? |
| Buyer changes software, branding or functionality after market placement. | Manufacturer obligations may be triggered depending on the change. | Does the change qualify as a substantial modification under the CRA and Commission guidance? |
Role classification must be confirmed for the exact commercial arrangement. A generic "CRA certificate" cannot replace access to the evidence and responsible people needed after launch.
Which Kitchen Appliances Need CRA Screening?
The CRA covers products with digital elements made available on the EU market when their intended purpose or reasonably foreseeable use includes a direct or indirect logical or physical data connection to a device or network. For a kitchen appliance, the screening question is not simply "Does it have Wi-Fi?"
| Product Configuration | Screening Priority | Reason |
|---|---|---|
| Mechanical appliance with no software, update interface or data connection. | Low | It may fall outside the product-with-digital-elements scope, but the specification should document why. |
| Digital appliance with embedded firmware but no declared connectivity. | Medium | Confirm whether service ports, update tools or reasonably foreseeable connections create a physical or logical data connection. |
| Bluetooth appliance controlled locally by a mobile app. | High | The appliance, app relationship and update pathway require scope and responsibility review. |
| Wi-Fi appliance with accounts, cloud recipes, remote control or OTA updates. | High | The appliance and relevant remote data processing solution may form one connected product system. |
| Connected appliance sold as a platform for third-party integrations. | High and complex | Interfaces, third-party components, support and vulnerability responsibilities need explicit mapping. |
Buyers should document connectivity, service interfaces, remote functions and update paths by SKU. Models using different wireless modules or firmware should not be treated as one cybersecurity configuration without evidence.
Buyers comparing connected and non-connected air fryer platforms can first review APEXDURA's smart Wi-Fi air fryer category and digital air fryer category to define which functions actually belong in the target specification.
The Supplier Evidence Pack to Request
| Evidence | Why It Matters | Practical RFQ Question |
|---|---|---|
| Product scope and role statement | Defines the connected functions, economic operator and responsible parties. | Which entity will place this SKU on the EU market under whose trademark? |
| Cybersecurity risk assessment | Connects foreseeable risks to security measures across design and maintenance. | Who performs and approves the assessment, and when is it updated? |
| Software component inventory or SBOM availability | Supports component vulnerability identification and technical documentation. | Can the supplier maintain a version-specific SBOM and provide controlled access when required? |
| Architecture and data-flow description | Shows how the appliance, app, cloud and third-party services interact. | Which functions stop working if the remote service is unavailable? |
| Coordinated vulnerability disclosure process | Defines how external and internal reports are received, assessed and remediated. | What public contact and internal escalation path will exist at launch? |
| Support-period rationale and end date | Defines how long vulnerabilities will be handled and updates provided. | What support period is proposed, what evidence supports it, and how will the end date be shown to buyers? |
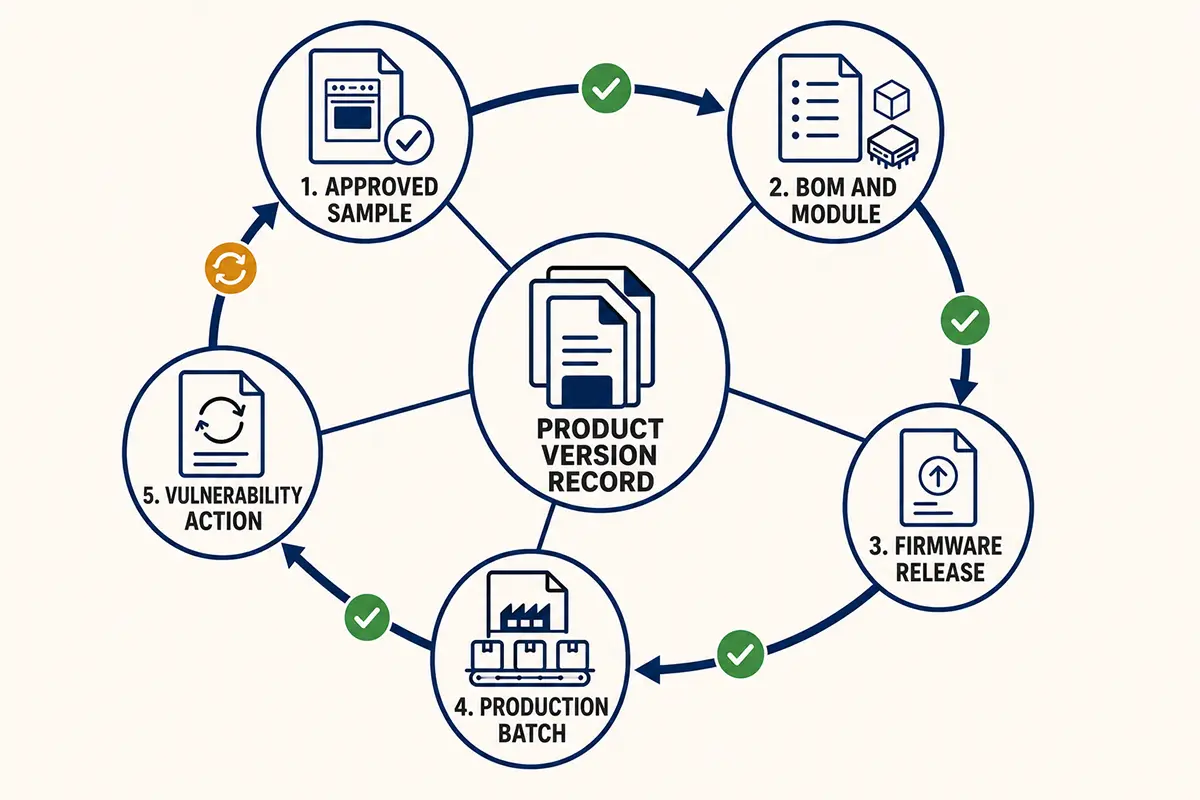
| Secure update and version-control records | Connects released firmware to approved samples, production lots and corrective actions. | How are firmware releases approved, signed, rolled back and traced to shipped batches? |
| Conformity and user-information plan | Aligns technical documentation, assessment, CE marking and secure-use instructions. | Who prepares the EU declaration, user instructions and final technical documentation? |
The CRA support period is generally at least five years, unless the product is expected to be used for less. Its end date, including month and year, must be clear at purchase. A commercial warranty period is not an automatic substitute.
CRA documentation should sit beside, not replace, the existing safety and radio evidence described in APEXDURA's CE documentation guide for European buyers. Connected models may also require separate attention to networked standby and energy settings; the ErP standby-power guide covers that parallel workstream.
Build CRA Gates Into the OEM Project
Connect cybersecurity decisions to the release gates already used for specifications, samples, components and production. APEXDURA's kitchen appliance production process shows why requests made after tooling, boards and packaging are fixed can affect several workstreams.
| Project Stage | Buyer Action | Supplier Evidence | Release Gate |
|---|---|---|---|
| RFQ | Map legal role, connected functions, app, cloud, support and target market. | Responsibility matrix and preliminary scope statement. | No quotation approval until software and lifecycle owners are named. |
| Supplier approval | Review security-development and vulnerability-handling capability. | Process descriptions, contacts, past release records and component-control method. | No supplier approval based only on price and traditional CE files. |
| Sample approval | Freeze hardware, wireless module, firmware, app build and cloud environment. | Version list, architecture, test scope and open-issue register. | No approved sample without a reproducible software configuration. |
| Pre-production | Confirm risk assessment, support period, update method and technical-file ownership. | Draft evidence index and reporting workflow. | No mass-production release while critical ownership remains unresolved. |
| Shipment and post-market | Link shipped batches to software versions and maintain vulnerability escalation. | Release record, batch mapping, user information and incident contacts. | No shipment if the actual software differs from the approved configuration without review. |
Reporting Readiness Cannot Wait Until 2027
From September 11, 2026, manufacturers must report actively exploited vulnerabilities and severe incidents affecting product security through the CRA Single Reporting Platform. The Commission describes an early warning within 24 hours and a fuller notification within 72 hours. For an actively exploited vulnerability, the final report is due no later than 14 days after a corrective or mitigating measure becomes available; for a severe incident, the final report is due within one month after the 72-hour notification.
Fast reporting requires the factory, firmware developer and cloud provider to identify the affected version, markets and corrective action. Contracts should define:
- who monitors reports and decides whether a CRA reporting threshold is met;
- who identifies affected firmware, components, SKUs, markets and batches;
- who communicates with the legal manufacturer and reporting workflow;
- who approves corrections and retains the decision evidence.
Reporting obligations apply to products with digital elements made available on the Union market, including products placed on the market before December 11, 2027. That is why a brand with connected appliances already in distribution should not limit its review to future launches.
Illustrative Scenario: A Private-Label Wi-Fi Air Fryer
This is a hypothetical example, not a customer case. An EU retail brand asks an overseas factory to supply a Wi-Fi air fryer under the retailer's trademark, while another provider supplies the app and cloud service. Although the retailer calls itself the importer, the CRA manufacturer definition may apply because it markets the product under its own trademark.
Before sample approval, the retailer should map appliance, app, cloud and update responsibilities; secure access to risk and technical evidence; define the support period; and link reportable vulnerabilities to affected batches. Later authentication or remote-control changes can then be assessed against a controlled baseline.
Common Mistakes and Red Flags
| Common Mistake or Red Flag | Possible Consequence | Better Practice |
|---|---|---|
| "We already have CE" is the complete cybersecurity answer. | Traditional files may not cover CRA lifecycle requirements. | Keep CRA evidence as a defined workstream linked to the wider conformity file. |
| The factory, app provider and cloud provider each point to another party. | No one owns reporting, support or remediation. | Sign a responsibility and escalation matrix before sample approval. |
| One firmware file is used across several SKUs without version mapping. | A vulnerability or correction cannot be scoped reliably. | Link firmware, wireless module, BOM, approved sample and production batch. |
| The support period is copied from a warranty period. | Commercial warranty and vulnerability-handling duties may be confused. | Document the CRA support-period rationale separately and verify the minimum rules. |
| The buyer waits for a final harmonised standard before doing any work. | Ownership and evidence gaps remain until late in the launch. | Start role, architecture, risk and process work now; update the assessment route as implementation develops. |
| The supplier offers a generic "CRA certificate" with no product version. | The document may not demonstrate compliance for the actual SKU. | Ask what assessment it represents, who issued it and which hardware, software and support configuration it covers. |
Honest Advice: Do You Need Connectivity?
Do not add Wi-Fi, cloud control or an app simply because the feature looks premium on a specification sheet. Connectivity creates software ownership, support, update, reporting, privacy and post-market work. If the target user gains little value from remote control, a mature non-connected platform may offer a lower-risk launch. If connectivity is essential, budget for the lifecycle responsibilities rather than treating the module as a small hardware option.
Limitations and Points to Confirm
This article is a sourcing guide, not legal advice. The final CRA role, product scope, conformity-assessment route, support period and effect of a modification depend on the exact product, software architecture, branding, contractual arrangement, intended use and target-market facts.
The July 27 guidance is non-binding and may be supplemented. Confirm the final route with qualified legal, cybersecurity and conformity-assessment professionals. Information was checked on July 28, 2026.
FAQ
Does every digital kitchen appliance fall under the CRA?
No. Scope depends on whether the product with digital elements is made available on the EU market and its intended or reasonably foreseeable use includes a direct or indirect logical or physical data connection. A model-specific assessment is still required.
Is the EU importer always responsible for manufacturer reporting?
No. The legal manufacturer carries the Article 14 reporting obligation, but a private-label EU business may itself meet the manufacturer definition. An importer also has duties when it becomes aware of vulnerabilities or believes a product is non-compliant.
Can buyers wait until December 2027?
No. Reporting obligations start on September 11, 2026 and can cover products already available on the EU market. Product architecture, contracts and supplier evidence also take time to correct.
Final Takeaway
The CRA turns a connected kitchen appliance into a lifecycle project. The physical factory, firmware team, app provider, cloud provider and EU economic operator need one controlled product definition and one workable path for risk assessment, support, reporting and corrective action.
Private-label buyers should classify their role, screen each SKU, request version-specific evidence and make cybersecurity ownership a pre-production release condition. APEXDURA's smart-appliance cybersecurity guide provides broader CRA and PSTI context, while its OEM and ODM project process helps define requirements by model.
Planning a connected kitchen appliance project for the EU?
Prepare your target market, product category, brand ownership, connected functions, app or cloud scope, expected quantity and launch date. Share those details through the APEXDURA project inquiry page so the team can discuss which supplier evidence and version-control checkpoints should be reviewed before sampling and mass production.