


0102030405
Smart Kitchen Sourcing 2026: Navigating the UK PSTI Act and EU Cyber Resilience Act (CRA) for Connected Appliances
2026-06-11
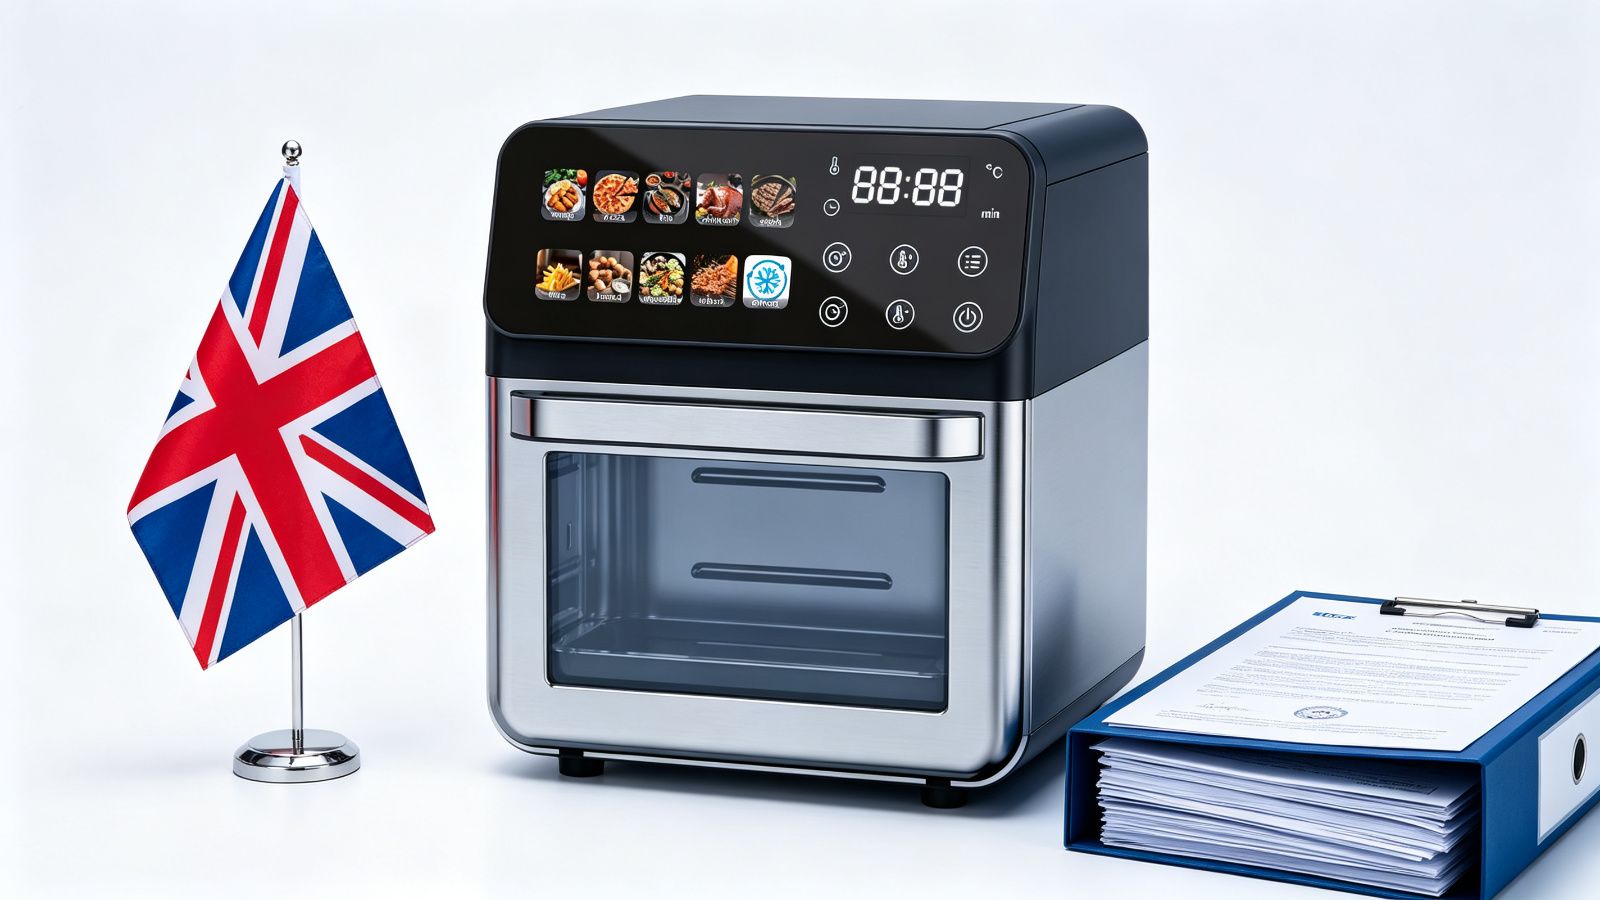
 Figure 1: The Connected Era. For today's smart home, a beautiful design must be backed by invisible, impenetrable cybersecurity architecture.
1. Executive Summary (BLUF)
As smart homes transition from a luxury niche to a mass-market standard, connected kitchen appliances—such as WiFi-enabled air fryers and precision coffee machines—have come under intense scrutiny from global cybersecurity regulators. The enactment of the UK Product Security and Telecommunications Infrastructure (PSTI) Act and the impending enforcement of the EU Cyber Resilience Act (CRA) represent a monumental shift. Legally, any smart home appliance that connects to the internet must now feature hardened, certified cybersecurity defenses. This is no longer an option; it is a strict prerequisite for customs clearance and retail distribution across Europe.
2. Key Facts Box: The IoT Security Landscape
Legal Enforcement: The UK PSTI Act is actively enforced, with fines of up to £10 million or 4% of global revenue for non-compliant brands.
European Standard: The EU Cyber Resilience Act (CRA) mandates a 3-to-5 year cybersecurity support window for all connected devices.
Vulnerability Reality: Over 40% of standard IoT appliances utilize weak, hardcoded default passwords, making them easy targets for botnets.
Strategic Advantage: B2B importers with certified smart products are capturing up to 30% higher margins in major retail tenders.
3. The "Ugly Truths" of Connected Appliance Sourcing
When sourcing smart appliances from traditional manufacturing hubs, B2B buyers often focus on the physical aesthetics of the machine while ignoring the digital risk.
1. The "Off-the-Shelf" firmware Trap
Many factories save on software engineering by using generic, unhardened Linux or FreeRTOS distributions. These firmware builds contain known vulnerabilities that have been documented for years. If your supplier cannot produce a Software Bill of Materials (SBOM), your brand is highly vulnerable to product safety recalls and PR crises.
2. The Shared Server Compromise
To keep cloud costs low, some low-cost suppliers host their mobile applications on shared, poorly configured cloud servers with inadequate database isolation. A leak on another client’s database can compromise your entire user base, exposing your brand to severe GDPR violations.
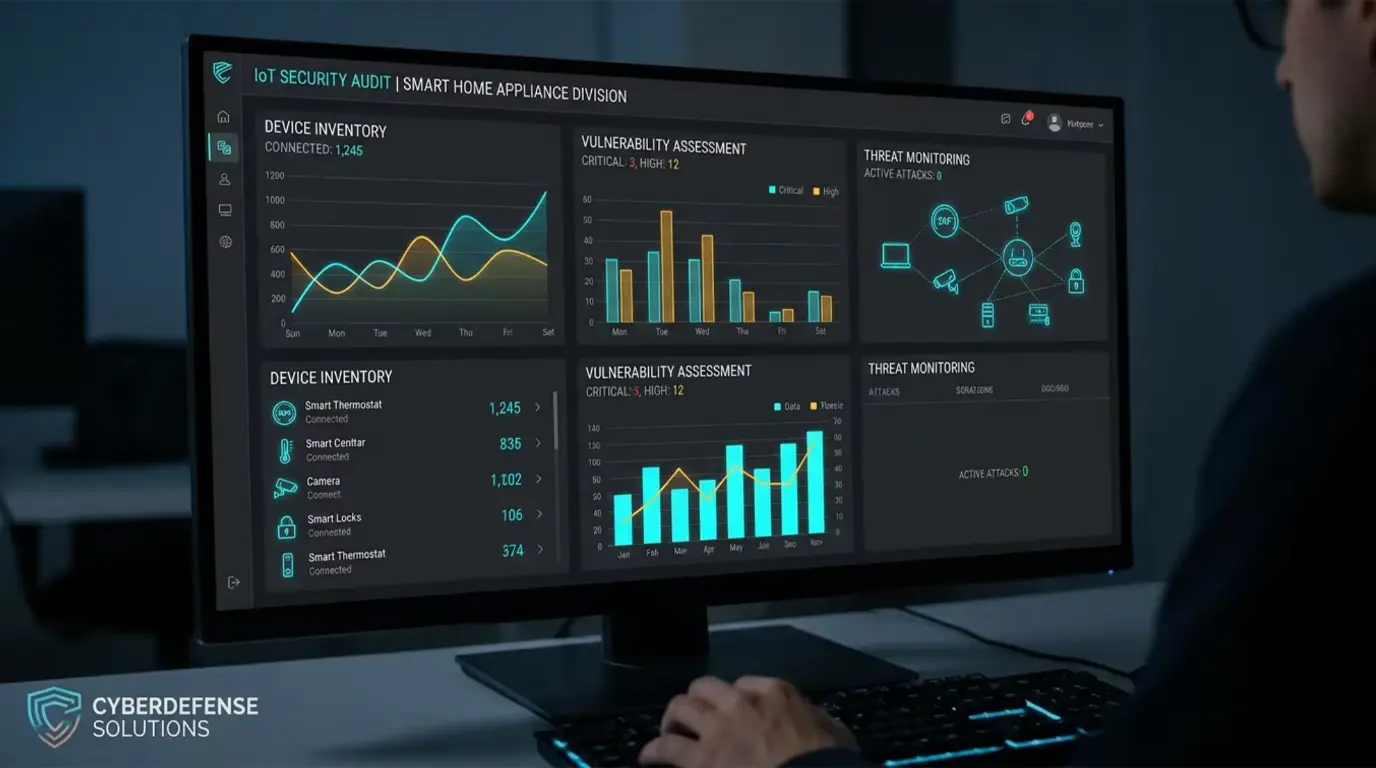 Figure 2: Digital Hardening. True IoT security is defined by continuous vulnerability scanning and robust threat mitigation at the server level.
4. Technical Module: Engineering the Secure Appliance
At APEXDURA, we designed our OEM/ODM connected platform to meet the strict demands of European and British cybersecurity standards. Our architecture is built around three core technical principles:
┌──────────────────────────────────────────────────────────┐
│                   APEXDURA SECURE IoT                    │
├────────────────────────────┬─────────────────────────────┤
│       DEVICE LEVEL         │        NETWORK LEVEL        │
│ • Hardware Root of Trust   │ • End-to-End TLS 1.3        │
│ • No Default Passwords     │ • Encrypted Cloud APIs      │
│ • Secure Cryptographic Boot│ • OTA Security Handshake    │
└────────────────────────────┴─────────────────────────────┘
No Default Passwords
Every smart appliance we produce is assigned a unique cryptographic identifier and a unique device password during assembly. We have eliminated standard default credentials (like "admin" or "1234"), rendering brute-force attacks impossible.
Secure Boot and Cryptographic Handshakes
Our control boards feature a Hardware Root of Trust. During startup, the secure bootloader verifies the digital signature of the firmware. If the code has been altered or tampered with, the system refuses to run. This prevents attackers from installing malicious firmware.
Encrypted Over-The-Air (OTA) Updates
A product that cannot be updated is a ticking security clock. Our cloud architecture supports secure, encrypted OTA updates. We use TLS 1.3 protocol with mutual authentication (mTLS) to push security patches to appliances in the field, ensuring they remain protected throughout their lifecycle.
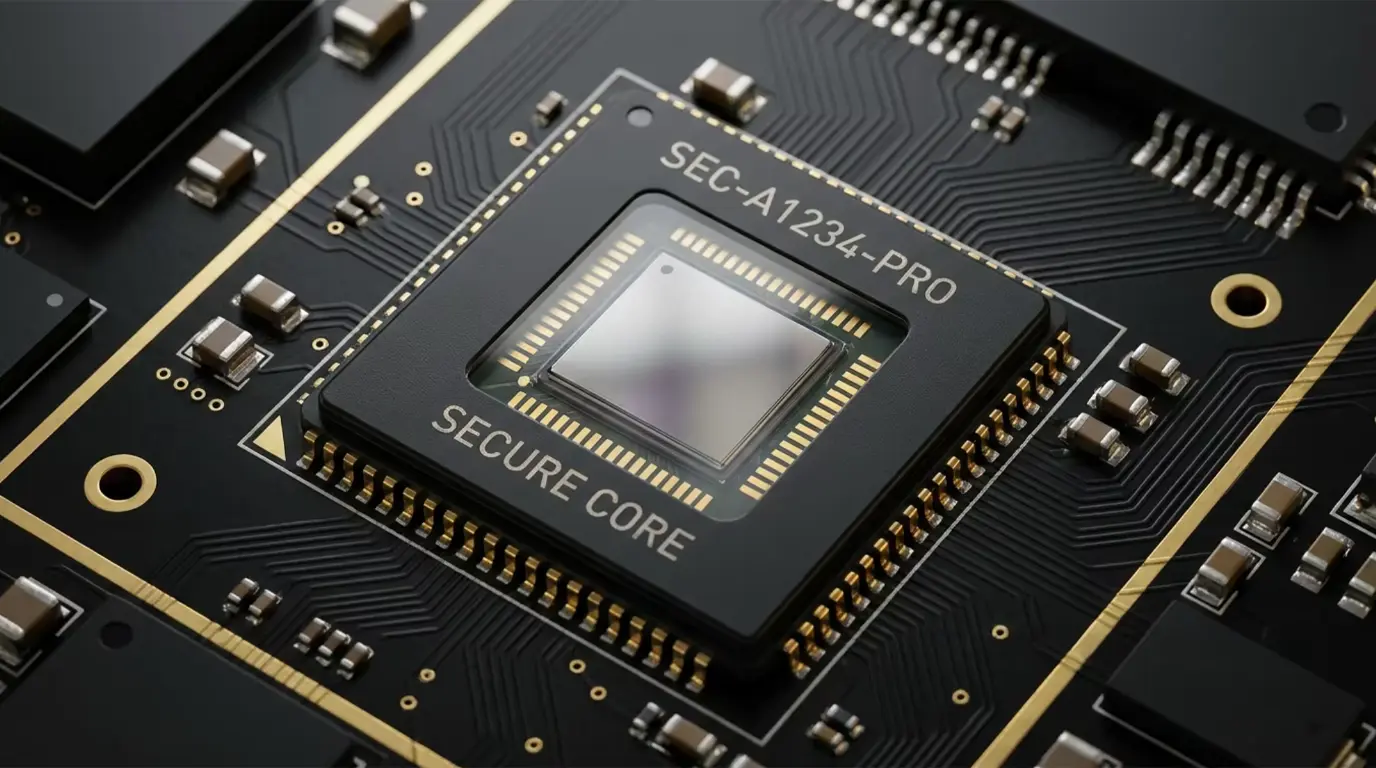 Figure 3: Hardware Root of Trust. APEXDURA control boards utilize dedicated security microcontrollers to encrypt and safeguard all user data.
5. Regulatory Comparison: UK PSTI vs. EU CRA
To help B2B buyers navigate the dual-regulatory landscape of Western Europe, we have compiled a detailed comparative analysis of the primary frameworks:
| Compliance Factor | UK PSTI Act (In Effect) | EU Cyber Resilience Act (CRA) |
|---|---|---|
| Geographic Scope | United Kingdom (England, Scotland, Wales) | European Union (27 Member States) |
| Core Directives | No default passwords, vulnerability disclosure, support periods. | Mandatory CE Mark, secure default settings, SBOM, active updates. |
| Support Transparency | Must state a clear support end-date on the packaging and site. | Guaranteed security updates for a minimum of 5 years (or lifecycle). |
| Penalties | Up to £10 Million or 4% of global annual turnover. | Up to €15 Million or 2.5% of global annual turnover. |
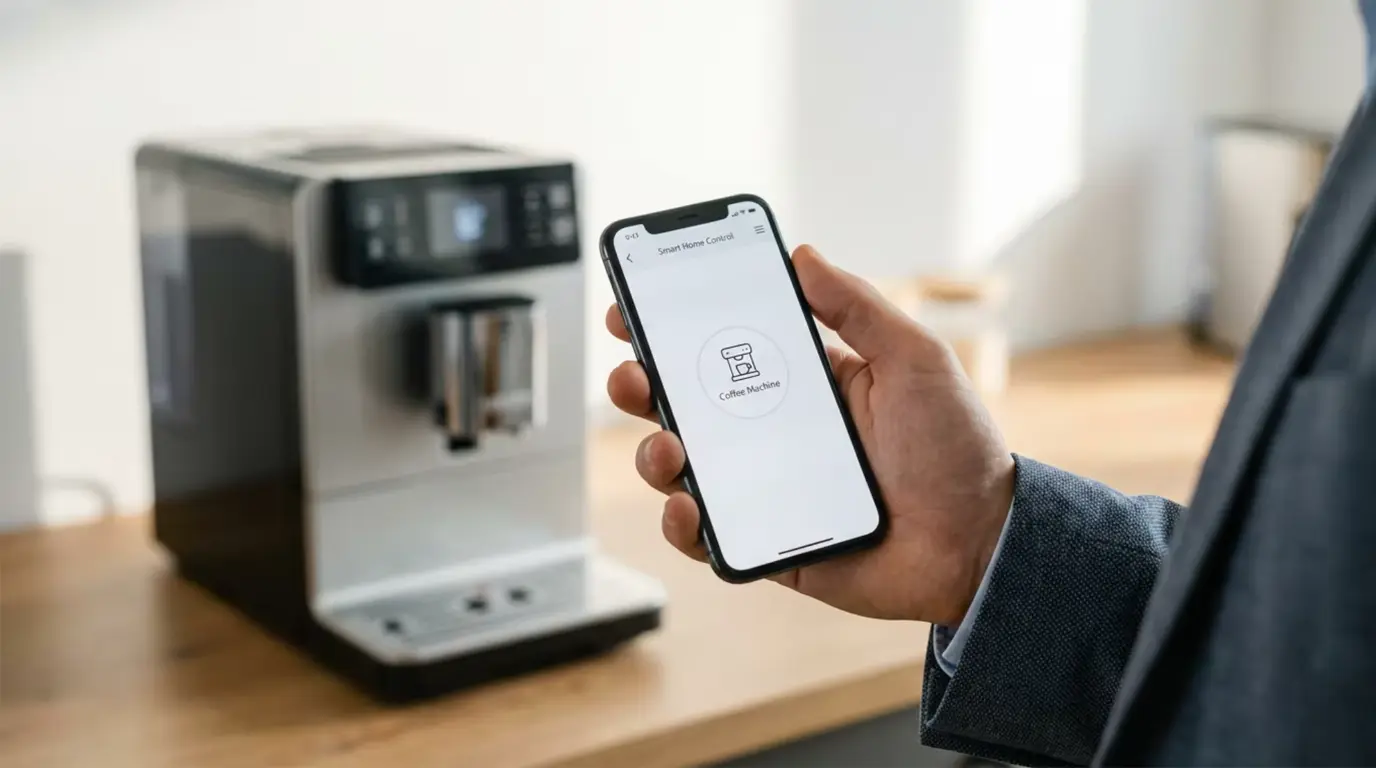 Figure 4: Seamless Control. A premium consumer experience requires an app that is as secure as it is beautifully designed.
6. Strategy for B2B Importers: The Compliance Audit Checklist
Before you place your next container order for smart WiFi kitchen appliances, require your manufacturer to complete this technical audit:
1. Request the Software Bill of Materials (SBOM)
A comprehensive SBOM lists all third-party and open-source software libraries utilized in the firmware. If a new vulnerability (like Log4j) is discovered, the SBOM allows you to immediately verify if your products are affected.
2. Validate the Vulnerability Disclosure Policy (VDP)
Under both PSTI and CRA, brands must have a public-facing page where security researchers can report vulnerabilities. This portal must be monitored, with a documented process for triaging and patching reported threats.
3. Confirm Third-Party Penetration Test Reports
Legitimate IoT manufacturers do not grade their own homework. Request recent, independent penetration test reports from accredited security laboratories (e.g., TUV Rheinland, DEKRA, or UL).
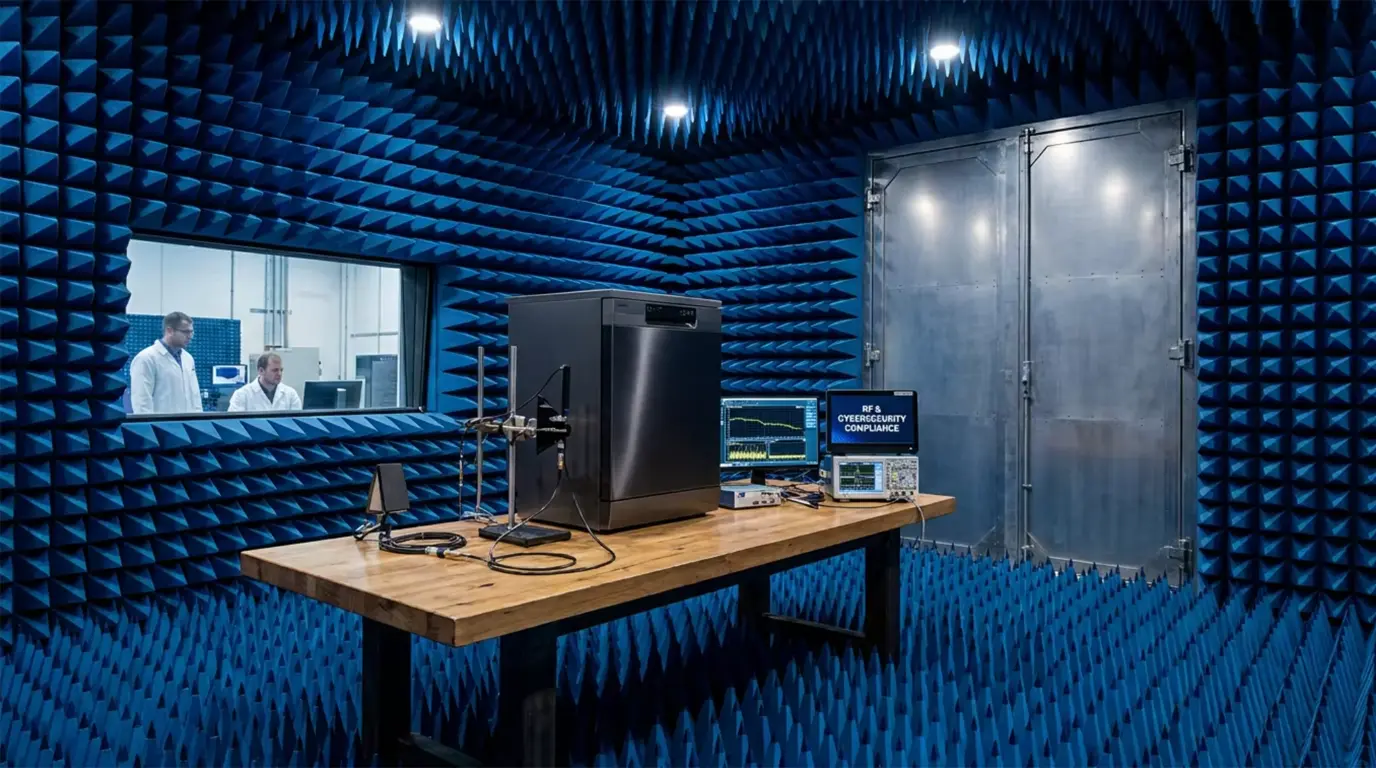 Figure 5: Rigorous Testing. Inside our state-of-the-art radio testing chamber, every connected appliance undergoes rigorous electromagnetic and wireless security audits.
7. FAQ: Key Cybersecurity Sourcing Questions
Do these cybersecurity regulations apply to appliances without WiFi, such as simple mechanical models? A: No. The UK PSTI and EU CRA specifically target "internet-connectable" products. Purely mechanical or offline electrical models (like our standard mechanical air fryers) are exempt from these security mandates.
How does security compliance affect the manufacturing timeline? A: When you partner with APEXDURA, there is no impact on your shipping timeline. Our baseline hardware and firmware platforms are already certified. We handle the technical file compilation during our standard OEM/ODM manufacturing cycle.
How do we market "Secure IoT" to premium consumers? A: Highlight privacy. The European consumer is highly protective of their personal data. Marketing your product as "Certified PSTI/CRA Cyber-Secure" is a powerful differentiator that builds long-term brand equity.